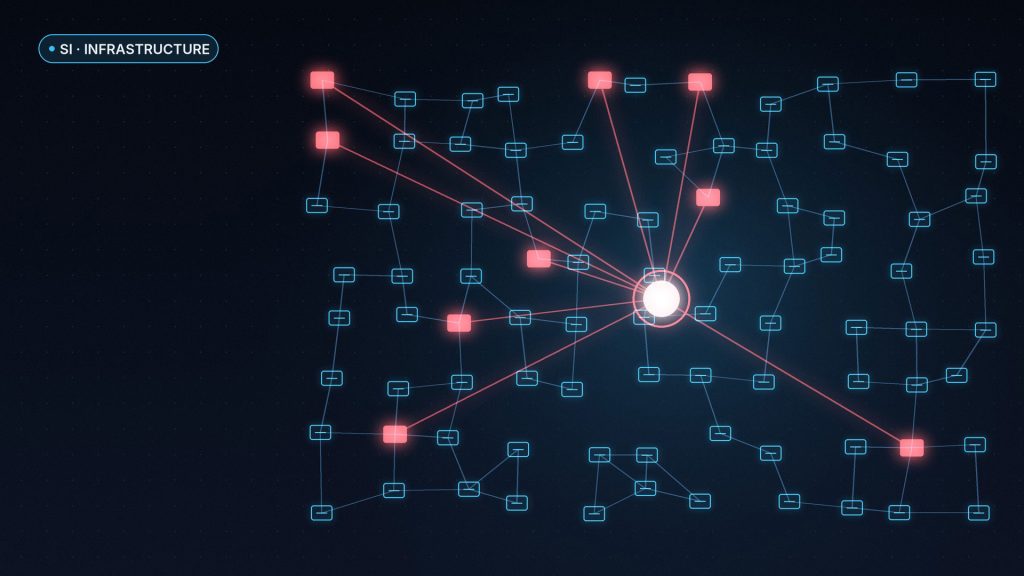
According to Symantec research published October 21, attackers have built an autonomous agent that hunts for unprotected SI endpoints and turns them into the brain of its operations.
Caught in a honeypot
Symantec set up a decoy SI service, left “unprotected” over the summer and captured the full instruction set of the agent making the requests. The decoy gathered over 127,000 requests from tens of thousands of IP addresses. Most of the traffic consisted of endpoint scanning, stolen-key spraying and-looking-for-exposed-config-file traffic.
How the agent works
- It seeks endpoints that accept OpenAI-style requests without authentication, or with a stolen key, including self-hosted models, gateways and MCP servers.
- Layered jailbreak prompts push the hijacked model past its safety rules.
- It carries 74 offensive tool definitions for reconnaissance, database theft, remote code execution and botnet control.
- A loop its creators call “Skynet mode” allows up to 100,000 unattended steps: scan, infect, mine crypto, repeat.
“The stolen model does not simply answer questions; it plans and drives the attack.”— Symantec
The honeypot executed none of the tools, and no confirmed compromises were tied to this agent. It proves intent, not damage. As Infosecurity Magazine notes, the victim ends up paying for the compute.
Lock it down
- Require authentication on every inference endpoint and gateway.
- Scope and rotate API keys.
- Restrict outbound traffic from model hosts.
- Tear down test deployments when experiments end.